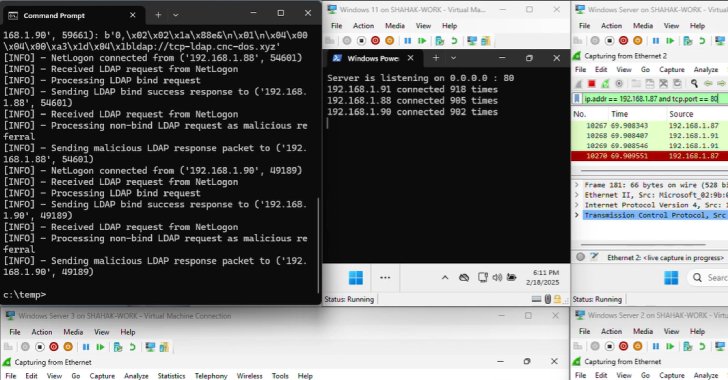
A novel attack technique could be weaponized to rope thousands of public domain controllers (DCs) around the world to create a malicious botnet and use it to conduct power distributed denial-of-service (DDoS) attacks.The approach has been codenamed Win-DDoS by SafeBreach researchers Or Yair and Shahak Morag, who presented their findings at the DEF CON 33 security conference today."As we
Source :
For further details, visit: https://thehackernews.com/2025/08/new-win-ddos-flaws-let-attackers-turn.html
Comments (0)
Be the first to share your thoughts on this story.